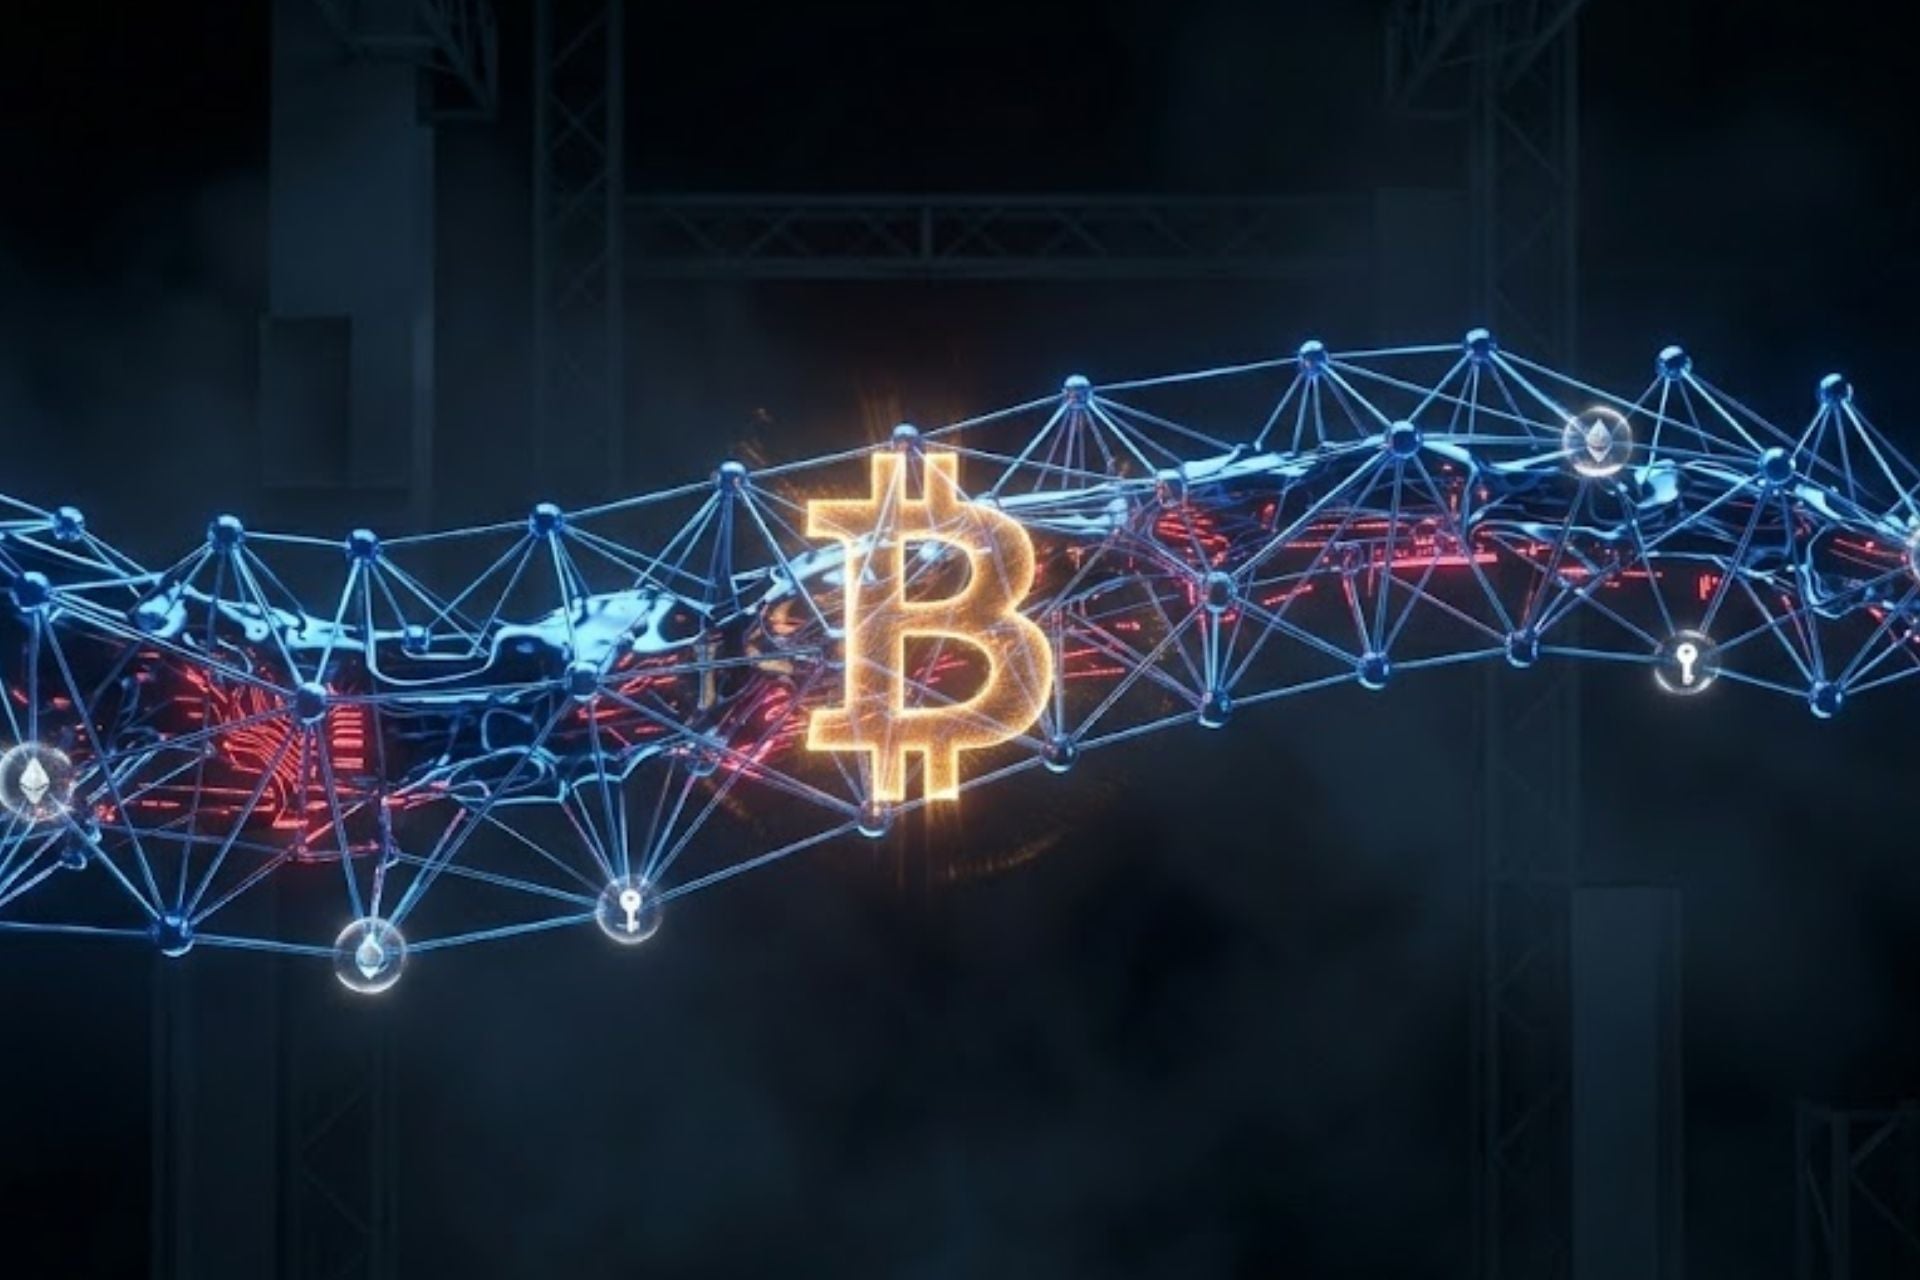
 © 01net with Gemini
A renowned researcher urges cryptocurrency holders to keep their funds “safe.” The researcher points to the rapid advances of generative AI in mathematics. These uncontrolled developments could weaken the digital signatures of wallets on the blockchain. In his view, investors’ cryptocurrencies could de facto be in danger within a few months. The warning is as divisive as it is prompting reactions.
Justin Drake, a renowned researcher at the Ethereum Foundation, the nonprofit organization behind Ethereum, urges investors to protect their cryptocurrencies without delay. On October 7, 2026, the expert called on the entire industry to prepare to enter “bunker mode.”In a long post published on X, he estimates that artificial intelligence could come to break the cryptography protecting Bitcoin, Ethereum, and other cryptocurrencies in the near future… well before the much-feared quantum computers.
“Today, I call upon the blockchain industry to calmly begin planning for ‘bunker mode’”, says Justin Drake on his X account.
Today I call upon the blockchain industry to calmly begin planning for “bunker mode”. My personal recommendation is to set in motion a controlled mass migration of assets to fresh addresses, i.e. addresses whose pubkeys remain hidden behind a hash.
Holders, starting with large and sophisticated ones, should consider moving the bulk of their funds to addresses that have never signed a transaction. And when they do sign one, they should also move remaining funds to a new address (possibly generated from the same seed phrase).
Don’t rush. While I believe there is cause for action a rushed migration would do more harm than good. Don’t panic either. Moving assets to protected addresses is a simple, preventative step which does not require new cryptography or new wallets.
IMO it is now reasonable to brace for the possibility that ECDSA breaks before qday, in the worst case in months not years. By “break” I mean fast private key recovery (e.g. in one week) on available hardware (e.g. a large GPU cluster).
Recent days have been humbling for human mathematical intuition. Long-held, unquestioned hypotheses have fallen. This includes the n log(n) bound for integer multiplication and the 3SUM conjecture.In hindsight, May’s unexpected disproof of the Erdős unit distance conjecture was our warning shot.
Yesterday’s OpenAI drop made it clear that mathematical superintelligence is upon us. They say there are weeks where decades happen. We are about to live through weeks where centuries of mathematical progress happen. Could our magic 64-byte ECDSA signatures be too good to be true? Was it just security through obscurity all this time?
Elliptic curves feel especially vulnerable to superintelligence. Curves carry rich structure, with room for fancy tricks like Schoof, Frobenius, pairings. (By contrast, hashes are designed to minimise algebraic structure.)
Separately, as Ewin Tang can attest, an efficient quantum algorithm sometimes foreshadows an efficient classical one. We should be open to the possibility of a classical counterpart to Shor that breaks elliptic curves and RSA at once.
Also noteworthy is the striking under-representation of cryptographic breakthroughs among the 722 mathematical results OpenAI published. I’ve witnessed first-hand the US government censoring academic quantum cryptanalysis results. Backroom interventionism is my base case.
I urge large, sophisticated actors to lead by example. Project11’s “risq list” (bitcoin-risq-list.projecteleven[.]com) is a great tracker of exposed BTC pubkeys. Binance, Bitbank, Robinhood, Bitfinex, and Tether have an opportunity to harden their cold storage. Next month I’ll address institutions in London in a live Q&A (forum.ethereuminstitutional[.]org/london-2026).
Again, please do not rush. Wallets holding under 50 BTC enjoy partial cover from “Satoshi’s shield”, i.e.his 20K exposed addresses that hold 50 BTC each. Load-bearing signers like oracles and L2 security councils should consider rotating ECDSA pubkeys with every signed message and/or multi-signing with a hash-based schemes like SPHINCS.
Exiting bunker mode safely will require post-AI cryptography. My inclination is to go all-in on hash-based cryptography and avoid structured mathematical assumptions entirely, whether from curves, lattices, or isogenies. A single battle-tested hash (e.g. from the SHA or BLAKE families) yields plausible post-AI security.
The Ethereum roadmap on strawmap[.]org fully embraces hash-based cryptography with end-to-end formal verification as a response to the quantum threat. Those timelines must now be revisited and accelerated in light of mathematical superintelligence. I’ll be pushing for maximum defensive acceleration.
— Justin Drake (@drakefjustin) October 7, 2026
An algorithm on the verge of collapse?
The researcher’s main concern involves ECDSA (Elliptic Curve Digital Signature Algorithm), the signature algorithm that secures the Bitcoin and Ethereum networks. This algorithm makes it possible to prove that a transaction was indeed approved by the owner of the wallet from which it originated, without the owner having to reveal their private keys. The algorithm works on the basis that a public key can easily be computed from a private key, but the reverse is practically impossible.You can therefore show your public key to everyone without risking malicious individuals deducing your private keys, which provide access to your crypto. For Justin Drake, the effectiveness of the algorithm is being called into question by the rise of AI.
“In my opinion, it is now reasonable to prepare for the possibility that ECDSA will be broken before Q-Day, in the worst case in a few months rather than a few years”, he wrote.
For reference, Q-Day refers to the day when quantum computers will be able to break current cryptography. The researcher believes that AI could enable attackers to quickly recover the private key of a wallet, “for example, in a week” with an army of graphics cards. In short, your cryptocurrencies would no longer be safe.
On to new addresses?
In this context, the researcher recommends that investors transfer their funds to new addresses that have never been used to make payments. According to him, “holders, starting with the largest and the most knowledgeable, should consider moving the bulk of their funds to addresses that have never signed a transaction”, he wrote. On these addresses, the public key has never been revealed. A hacker therefore has no way to guess the private keys, even if they managed to compromise the algorithm.
“Don’t rush. Even if I think action is warranted, a hasty migration would do more harm than good. Don’t panic either,” declares
The researcher also appeals to major platforms such as Binance, Robinhood, Bitfinex, and Tether, urging them to strengthen their storage solutions that are not connected to the internet. He nevertheless acknowledges that people who hold few cryptocurrencies will probably not be targeted by hackers who manage to crack the algorithm. Instead, they are likely to go after the big fish, including the various accounts of Satoshi Nakamoto, the creator of Bitcoin.
Vitalik Buterin, co-founder of Ethereum, urges caution and recommends not giving in to panic. He considers it “very easy to lose funds because of a hasty and poorly configured upgrade,” and even admits that failed migrations have cost him more than hackings have. This is not the time to act hastily.
Also read: North Korean hackers use the Ethereum network to launch cyberattacks
OpenAI sets the world on fire
Justin Drake’s warning did not come out of nowhere. On October 6, OpenAI published 722 mathematical manuscripts produced by an internal AI model. Among the AI’s work, some overturn hypotheses that are several decades old.Note that ChatGPT already solved a 200-year-old equation last month. “Yesterday’s OpenAI publication clearly showed that mathematical superintelligence is here,” according to Justin Drake.
“There are weeks when decades happen. We are on the verge of experiencing weeks when centuries of mathematical progress happen,” the researcher says.
According to Drake, mathematical elliptic curves, on which the ECDSA algorithm is based,“seem particularly vulnerable to the superintelligence” demonstrated by OpenAI’s models. This past summer, Anthropic also revealed that Claude Mythos Preview had found a vulnerability in HAWK, an algorithm designed for post-quantum computing, within 60 hours. This proves that AI is already capable of breaking algorithms, even if there is no indication that the ECDSA algorithm is vulnerable. The researcher says it will not be long before AI poses a threat to the mathematical algorithms that secure cryptocurrencies.
Also read: $351 million in cryptos stolen – the Bitget platform was hacked by North Korean hackers
A controversial warning
Not all security experts share Drake’s assessment.For Charles Guillemet, Ledger’s chief technology officer, advances in AI, although “truly bewildering for our past intuitions,” do not mean that the algorithms at the heart of blockchain security are in danger in the near future. He believes that “treating a classical ECDSA break within a few months as a working assumption still amounts to FUD”, that is, an attempt to sow fear in the markets.
Impressive work from the recent math drops, the unit-distance counterexample, the sub-n log n multiplication result, and the 3SUM/APSP improvements are genuinely humbling for prior intuitions.
That said, treating a classical ECDSA break in months as a planning baseline still looks like FUD.
A practical private-key recovery attack on secp256k1 (or similar curves) on available hardware would not stay confined to Bitcoin and Ethereum. It would compromise TLS, code signing, most banking systems, and a large fraction of deployed public-key infrastructure at once.
Hash-based schemes are attractive precisely because they minimize algebraic structure, but the same loss of mathematical intuition that motivates caution on curves also applies to hashes 😉
A calm hygiene improvement (avoiding address reuse after the first signature) is reasonable for large holders, and all good wallets incentivizes using new addresses.
But calling for a “mass migration” would create operational mistakes that lose funds with higher probability than the scenario being mitigated.
We already have a Post Quantum migration to execute, let’s not add more confusion.
— Charles Guillemet (@P3b7_) October 7, 2026
The cryptographer emphasizes that an attack of such magnitude“would not be confined to Bitcoin and Ethereum”. An attack capable of breaking the ECDSA algorithm would endanger“ most banking systems and a large portion of the deployed public-key infrastructure.” It would therefore be a disaster for the entire system, not just cryptocurrency.
Nevertheless, Charles Guillemet does not reject all the measures proposed by Drake. “For large holders,” it is better to avoid reusing an address after a first transaction, as a security precaution. He firmly rejects the idea of a “mass migration,” intended to abandon addresses already used in transactions.A migration of this scale risks having the opposite effect. Owen Simonin, a crypto entrepreneur better known under the pseudonym Hasheur, also reacted to the warning. He emphasizes that this is only a “hypothesis”, and “not a demonstrated vulnerability”.
I don’t recommend anyone scramble to move their funds to new wallets today. But we should take the risks to cryptography from AI-accelerated math seriously, and minimize our exposure to not just quantum-vulnerable cryptography, but also potentially AI-vulnerable cryptography.
The core new area of risk from this viewpoint is, unfortunately, ML-DSA / FHE / lattices.
(and it’s also another reason, along with quantum, why ECDSA might fall even faster than expected, hence the “fresh address” recommendation)
So far most people have been in the mode of thinking “elliptic curves broken, hashes safe, lattices safe”. But there is a good chance that the concrete security of lattices will take serious hits from the next two years of AI math.
The basic threat model is: factoring is something that naively takes 2^(n/2) time, but over decades smart people have found and optimized number field sieves, and degraded that to 2^O(n^(1/3)), which is why RSA keys and signatures need to be ~400 bytes (and not 64 bytes).What if there are skeletons in the closet like that, both for elliptic curves and lattices, that we are simply not smart enough to discover – but bots soon will be?
This is a major part of the reason why for the past year ethereum’s lean roadmap has been going in the “hash-only” direction: no lattices, no ML-DSA, no Falcon, no lattice-based commitments inside ZK proofs, etc. Signatures in lean ethereum are all hash-based, either WOTS or SPHINCS-.
For signatures and proofs, we already know how to go hash-only. The bigger challenge is for *public-key encryption* – and this goes far beyond blockchains. Secure communication, anonymizing protocols, lots of things need public-key encryption.
And unfortunately there are long-standing mathematical theorems showing why public-key encryption cannot be done with hashes alone. You have to have some kind of trapdoor object that has at least one form of usable “structure” – either group theory (incl. isogenies) or lattices or code-based or potentially in the future even more newfangled and spooky things (local mixing?). But for anything that has structure, you should assume that AI will make at least some progress in breaking that structure. Here, one reasonable inference is that if you want to make something plausibly long-term secure, multiply the key sizes by 10.
To me that’s a very plausible world and something not at all extreme to predict. If AI will bring us 50 years of math in 2 years, then that 50 years of math may very plausibly include a “naive factoring -> GNFS” level of improvement to our ability to break lattices.In that world, lattices will still exist, but they will have to be significantly bigger to guarantee the same level of safety.
And at those new larger sizes, hash-based constructions will beat lattice-based constructions on concrete efficiency in every use case where hash-based constructions are possible at all.
Theoretically, of course it’s possible that hashes are broken too (eg. P = NP would imply that). But I think P = NP is very unlikely. And intuitively, it’s much more likely that a mathematical object has exactly no exploitable structure (like hashes are intended to), than that a mathematical object has exactly ~3 forms of exploitable structure (for elliptic curves: associativity, Schoof, pairings) and not some secret fourth form of structure we have not yet discovered that greatly degrades its security (for elliptic curves, ECDLP and pairing security). Similar for LWE, SVP, RLWE and the zoo of lattice problems.
For this reason, we do not yet see any reason to worry and start padding the byte size of hashes (if we start to worry more, we would pad the round count first before doing anything to the byte size).
Concrete TLDR, my own personal views:
* Hash-based > lattice-based, in those situations where hash-based is possible at all
* For anything lattice-based, be much more paranoid on param sizes. Remember that blockchains are only a small portion of the cryptography story; this point goes far beyond blockchains and applies to eg. access to websites, secure messaging, Tor / VPNs …
* For privacy protocols, strongly favor NOT putting encrypted notes onchain.Instead, send them offchain through some third-party mechanism.
* If it’s not difficult for you, keeping your funds in addresses which have not yet been used to make a transaction is a good idea. If it’s easy for you, do it. **But be careful about migrations; I personally have lost more money in botched migrations than I have lost in all hacks combined**.
* For multisig wallets, doing confirmations offchain is better than onchain, because this way the signatures of signer wallets do not get exposed to the public, so if ECDSA falls to AI much faster than expected, at least the multisig “gracefully degrades” to a 1-of-1 where the 1 is whoever was gathering the signatures – a much better place to be than “anyone can take the money”
https://t.co/oVjwZog2lL— vitalik.eth (@VitalikButerin) October 7, 2026
Even if there is “a strong possibility that the practical security of the networks will be seriously undermined by advances in AI in computing over the next two years”, there is “no reason to worry for the time being”, says Vitalik Buterin, who has devoted several publications to Justin Drake’s remarks. For the time being, no known attack can break ECDSA, whether using AI or a quantum computer.
👉🏻 Follow tech news in real time: add 01net to your sources on Google, and subscribe to our WhatsApp channel.

- Google Play Store
- 4K Video Downloader Plus
- VLC Media Player
- Adobe Reader
- uTorrent
- WinRAR
- Xender
- Google Chrome
- CCleaner
- Mozilla Firefox
- Avast Free
- ChatGPT
- Microsoft 365
- Opera One
- Avast One


Download
- Google Play Store
- 4K Video Downloader Plus
- VLC Media Player
- Adobe Reader
- uTorrent
- WinRAR
- Xender
- Google Chrome
- CCleaner
- Mozilla Firefox
- Avast Free
- ChatGPT
- Microsoft 365
- Opera One
- Avast One


