Yasukuni Shrine (Chiyoda Ward, Tokyo) announced on November 11 that approximately 14,500 records of personal information had been leaked due to unauthorized access to the mail-order website “Online Amulets and Religious Articles Site,” which is operated by the shrine. The site is currently suspended, and the timing of its resumption has not yet been determined.
 (Source: Official website)
The information leaked included names, email addresses, hashed passwords and the auxiliary information used to generate them, and administrative information such as member account registration dates and usage status. Although the passwords cannot be read as they are stored, there is a risk that a third party could determine the original passwords. The number of records affected is still under investigation and may change in the future.
As of the 11th, no leakage of credit card information, addresses, telephone numbers, dates of birth, purchase histories, or similar data had been confirmed. No secondary damage resulting from this leak had also been found.
The shrine detected the unauthorized access on October 28 and suspended the website that same day. It is currently investigating the cause and the scope of the impact together with the website management company.
The shrine plans to contact each affected person individually by email. It is urging users who use the same password for the website and other services to change their passwords promptly. It is also warning people to be on guard against suspicious communications that misuse the leaked names and email addresses and impersonate the shrine.
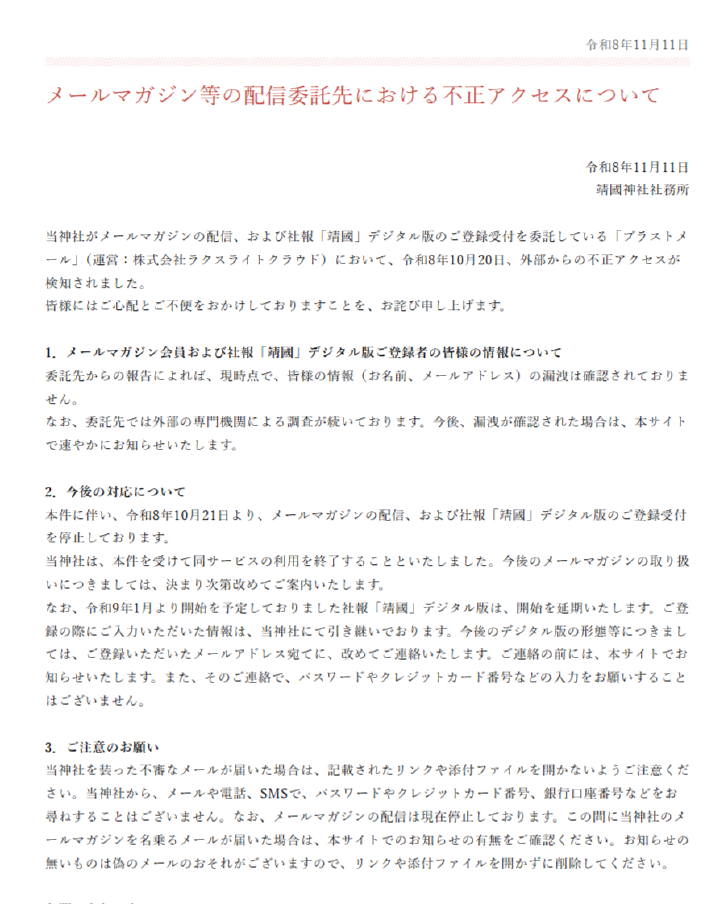 Full press release