On November 9, Edion announced, in a follow-up to the unauthorized access to its e-commerce site disclosed on November 6, that an unauthorized program had been embedded in its payment processing, and that information including credit card numbers and security codes entered on the payment screen from a PC may have leaked to third parties in as many as 556 instances.
It also announced that, in exceptional cases, up to five records containing card numbers and security codes may also have leaked when the input details were temporarily recorded in the system log after an error occurred on the order screen.
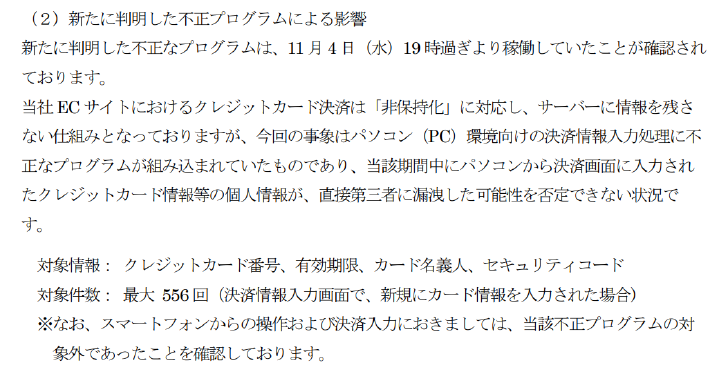 From Edion’s timely disclosure dated the 9th. Possibility of leakage through the unauthorized program
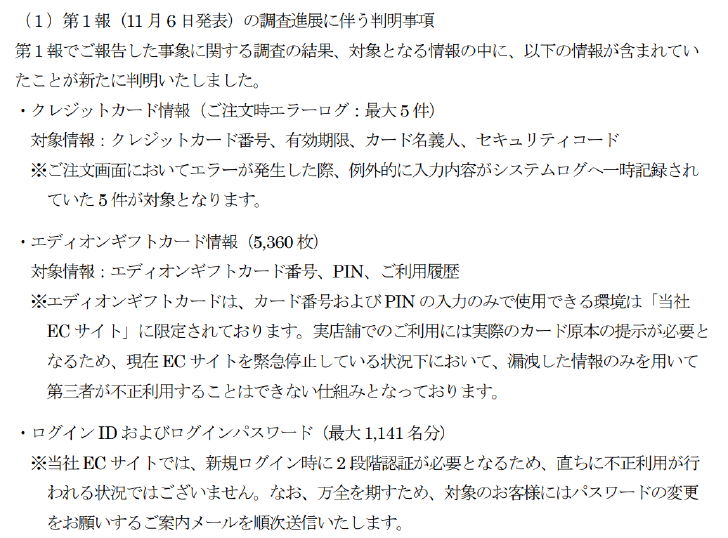 Possibility of leakage through the logs
The company had adopted a system that does not retain card information on its servers, and had stated in its initial report on the 6th that card numbers were not included among the potential data leaks, but a new possibility of leakage has since been identified.
Card numbers, expiration dates, cardholder names and security codes may have leaked through the unauthorized program
The unauthorized program was embedded in the payment-information entry process for PCs and began operating shortly after 7 p.m. on November 4. Operations and payment entry from smartphones were not subject to the unauthorized program.
The 556 figure is the maximum number of instances in which new card information was entered on the payment-information entry screen. The information targeted included the credit card number, expiration date, cardholder name and security code.
Five pieces of card information saved in the log when an error occurred may also have leaked
A subsequent investigation into the unauthorized access reported in the first report found that the potential data leaks may have included up to five pieces of credit card information, information on 5,360 Edion gift cards, and login IDs and login passwords for up to 1,141 people.
The card information consisted of input details that, in exceptional cases, were temporarily recorded in the system log when an error occurred on the order screen, and included the card number, expiration date, cardholder name and security code.
Gift card information comprises the card number, PIN and usage history. The future handling of gift cards is under consideration. Emails requesting password changes will be sent one by one to those whose passwords may have leaked.
In the first report: “No leakage of card numbers had been confirmed”
In the first report on the 6th, Edion announced that unauthorized access from outside had exploited a system vulnerability in part of the server area where log files for the e-commerce site were stored, and that personal information for up to 4,131 people and order information for up to 9,554 people may have leaked.
At that point, the company had not confirmed any leakage of credit card numbers or login passwords, but subsequent monitoring and investigation revealed traces of new unauthorized access.
To prevent the damage from spreading, the company placed its e-commerce site, the Edion official app and the Edion Smart app under emergency suspension at 10 p.m. on November 7. The resumption of the e-commerce site has not been decided.

