Umilink (Shibuya Ward, Tokyo), an email delivery service provider, announced on November 11 that a total of 47,860,147 pieces of personal information, including email addresses, had been leaked externally in connection with the unauthorized access it disclosed on October 19. As of October 26, the company had said that as many as approximately 51.62 million records might have been leaked, but it subsequently reassessed the number through further investigation. Several companies using its email service have successively disclosed the impact since late October.
The breach affected 49 systems of the company’s email delivery service, “Cuenote FC.” The information leaked included 47,860,147 email addresses, 30,500,167 membership IDs, 6,665,055 names, 2,059,658 pieces of gender information, 949,217 dates of birth, 412,794 telephone numbers, and 1,823,551 postal codes. It also included prefectural names, addresses, hashed passwords, company names, school names, and authentication information for services operated by customers.
In its October 26 announcement, the company also revealed that a total of 190 records—including contracting company names, names, telephone numbers, and email addresses—had been accessible from outside the customer management system, “Cuenote BASE.”
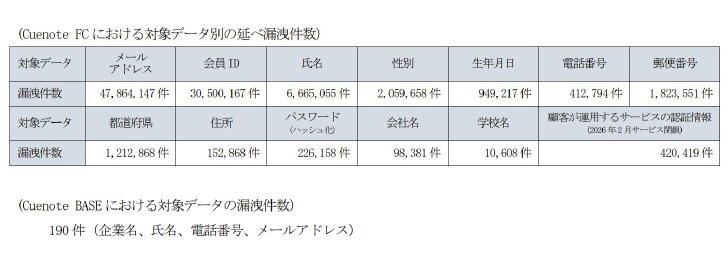 List of leaked information (press release)
According to Umilink, the attacker exploited a vulnerability in the system, planted an unauthorized program on the server to access the database, stole information indicating users’ logged-in status, impersonated legitimate users, and extracted data through the administration screen. The company detected the unauthorized access on October 16 and began addressing the vulnerability and removing the unauthorized program.
Currently, all services other than some systems of “Cuenote FC” and “Cuenote BASE” are operating normally. The company plans to introduce measures such as AI-powered source code reviews and round-the-clock, 365-day monitoring to prevent recurrence. It intends to publish the results again after completing the final investigation by an external specialist organization.
As companies using the service successively disclosed information leaks, the full extent of the impact became clear. iStyle, which operates the cosmetics review site “@cosme,” announced on November 9 that customer information on approximately 2.8 million people had been leaked. JR Central and two other companies also announced on the 5th that a total of approximately 170,000 membership records had been leaked through the Shinkansen reservation services “Smart EX” and “Express Reservation.”

